Sovereign cybersecurity for your network and every endpoint in your business.

PulpShield detects and stops the advanced attacks antivirus never sees — command-and-control, data exfiltration, lateral movement — from one lightweight agent. A 100% French solution, hosted in France 🇫🇷, deployable on your own servers with no foreign cloud. Sovereign AI analysis available as an option.

🇫🇷 French-built, hosted in France Converged NDR + EDR Optional AI analysis Free 3-month trial
Why now

In 2026, AI is changing the scale of the cyber threat

Hyper-realistic phishing, deepfakes, automated attacks: the technical barrier is collapsing. Small and mid-sized businesses are on the front line — and many never recover from a serious breach.

⚠️
A successful attack can be fatal to a small business. This is no longer about inconvenience — it is about survival. Europe needs sovereign tools to protect its economic fabric.
The solution

One lightweight agent per endpoint, one console to watch everything

🛰️

NDR — Network

Passive traffic analysis: detects command-and-control traffic, data exfiltration, scanning and lateral movement.

🖥️

EDR — Endpoints

Process and command telemetry: catches system tools being abused, and reverse shells.

🪶

Frugal — Rust

A native agent with a very small CPU and memory footprint, on Windows, Linux and macOS — it does not slow the machine down.

Strengths

What PulpShield brings that others do not

🧠

Behavioural detection

13 detectors — C2 beaconing, DGA, exfiltration, brute force, cryptomining and more. Every alert is scored and explained.

🤖

AI analysis — optional

As an option, a sovereign AI — Mistral models running on your own servers — reviews the collected data to rule out false positives and suggest what to do next.

🇫🇷

Full sovereignty

Fully deployable on-premise. Your data stays with you — from the network all the way to the AI. GDPR compliant.

🛡️

One-click response

Block a malicious address or isolate a compromised machine straight from the console.

🌐

Complete visibility

Network map, discovery of unmanaged connected devices (printers, cameras, IoT), and a full detection journal.

📋

NIS2 & CRA compliance

Detection, incident traceability and reporting — to meet NIS2, CRA and GDPR obligations, at a scale an SME can handle.

🍯

Intruder traps

Invisible decoys only an attacker can trip: a near-certain alert, with almost no false positives.
Innovation

AI analysis, optional: fewer false alarms

For a small business the hard part is not detecting — it is knowing whether an alert is real, and what to do about it. PulpShield offers, as an option, an analysis layer built on Mistral AI models running on your own servers. It draws on the data the agent already collects: alerts, reputation, baseline and correlation across machines.

  1. 1
    The endpoint detects an anomaly and sends the alert, with the relevant logs, to the central console over a secure channel.
  2. 2
    The AI reviews the context — logs, reputation, baseline, correlation across machines — and decides: real alert or false positive.
  3. 3
    Everything is recorded in the journal: the verdict, the reasoning and the timestamp — ready for audit and compliance.
  4. 4
    If the alert is real, the AI talks your technician through it, step by step, from the checks to the actions.

Less noise, more signal

Traditional tools drown small teams in false positives. Once enabled, the AI analysis filters the noise and turns each genuine alert into a clear plan of action — like a SOC analyst, at a scale an SME can afford.

Sovereign: the AI runs on your own servers using open-weight Mistral models — no sensitive data is ever sent to a foreign LLM.

Sovereignty

The only sovereign alternative designed for smaller businesses

Almost every market leader is American or British, and most require their cloud. PulpShield is 100% French, published and hosted in France 🇫🇷, and deployable on-premise: your data never leaves your own infrastructure.

SolutionOriginCloud requiredEU sovereignty
CrowdStrike, SentinelOne🇺🇸 United StatesYesNo
Microsoft Defender🇺🇸 United StatesYesNo
Darktrace🇬🇧 United KingdomOftenNo
Stormshield🇫🇷 FranceNoYes
PulpShield🇫🇷 FranceNoYes

Positionnement indicatif par catégorie. PulpShield is the only product combining NDR and EDR in this sovereign category for the SME segment, with AI analysis available as an option.

SOC capability, SME budget

The benefits of a SOC, without building one

Detection, incident correlation, response and AI triage: PulpShield automates the core functions of a security operations centre. Your business is protected without a team of analysts.

Running an IT services business (MSP)? Monitor every client from a single console and operate your own managed SOC.

👁️ Continuous monitoring

Round-the-clock detection across network and endpoints.

🤝 Automated triage

The AI handles the first-line analyst work.

🏢 Multi-tenant (MSP)

One console for dozens of client businesses.

Regulatory compliance

Ready for NIS2 and the Cyber Resilience Act (CRA)

European regulation is tightening, and now covers thousands of small and mid-sized companies. PulpShield helps you meet those obligations — detection, traceability, evidence.

🇪🇺

NIS2 Directive

Thousands of companies and public bodies must now detect and report security incidents. PulpShield provides the advanced detection, incident traceability and reporting that compliance requires.

🛡️

Cyber Resilience Act (CRA)

The CRA mandates security for connected products placed on the European market: secure by design, vulnerability management, updates. PulpShield monitors your systems and is itself built on those principles — a memory-safe language (Rust) and full data sovereignty.

PulpShield is a compliance aid: it supplies the detection, traceability and evidence NIS2 and the CRA expect. It does not replace your wider compliance programme.

Pricing

Enterprise-grade protection at an SME price

Download it and try it free for three months, then subscribe per endpoint — with no hardware commitment. Data hosted in France 🇫🇷.

Starter

6 € per endpoint / month

1 to 10 endpoints

  • NDR + EDR agent
  • Dashboard & journal
  • One-click response
  • Email support
Choose
Recommandé

Business

5 € per endpoint / month

11 to 50 endpoints

  • Everything in Starter, plus
  • AI analysis (Mistral) — optional
  • Central console
  • NIS2 compliance
Choose

Pro

On request

50+ endpoints / regulated sectors

  • Everything in Business, plus
  • On-premise deployment
  • SLA & priority support
  • Integrations
Contact us

MSP

Partner

IT service providers

  • Multi-tenant console
  • Wholesale pricing / white label
  • Training & tooling
  • Shared recurring revenue
Become a partner

Indicative pricing, excluding tax, subject to confirmation. Volume discounts and MSP rates on request.

See it before you install it

The monitoring interface, with nothing to install

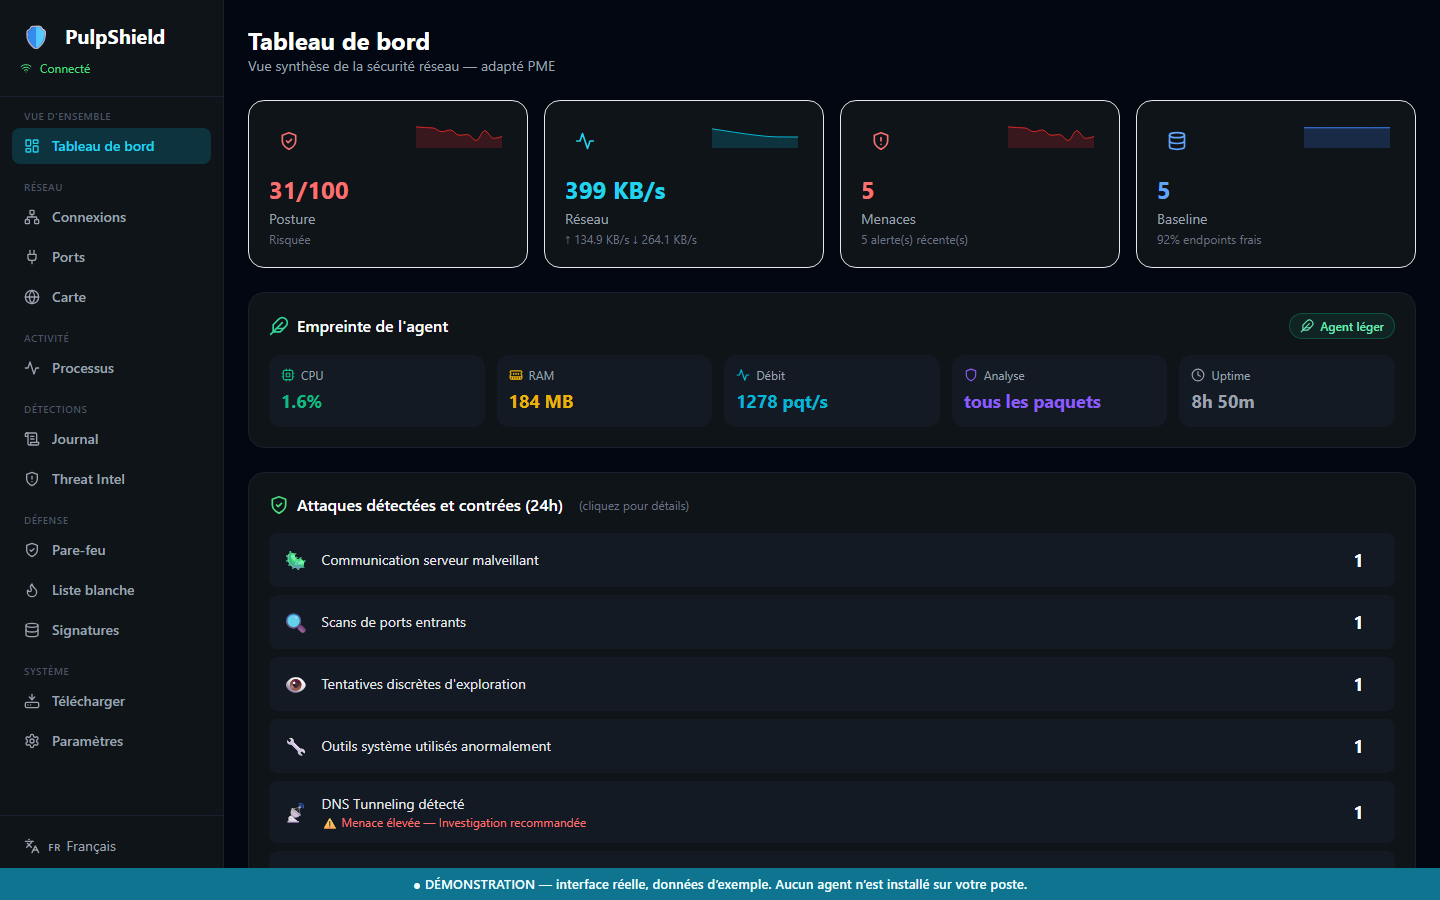
A dashboard a business owner can read, not just a specialist. Every alert is explained in plain language, with the process at fault and where it was talking to.

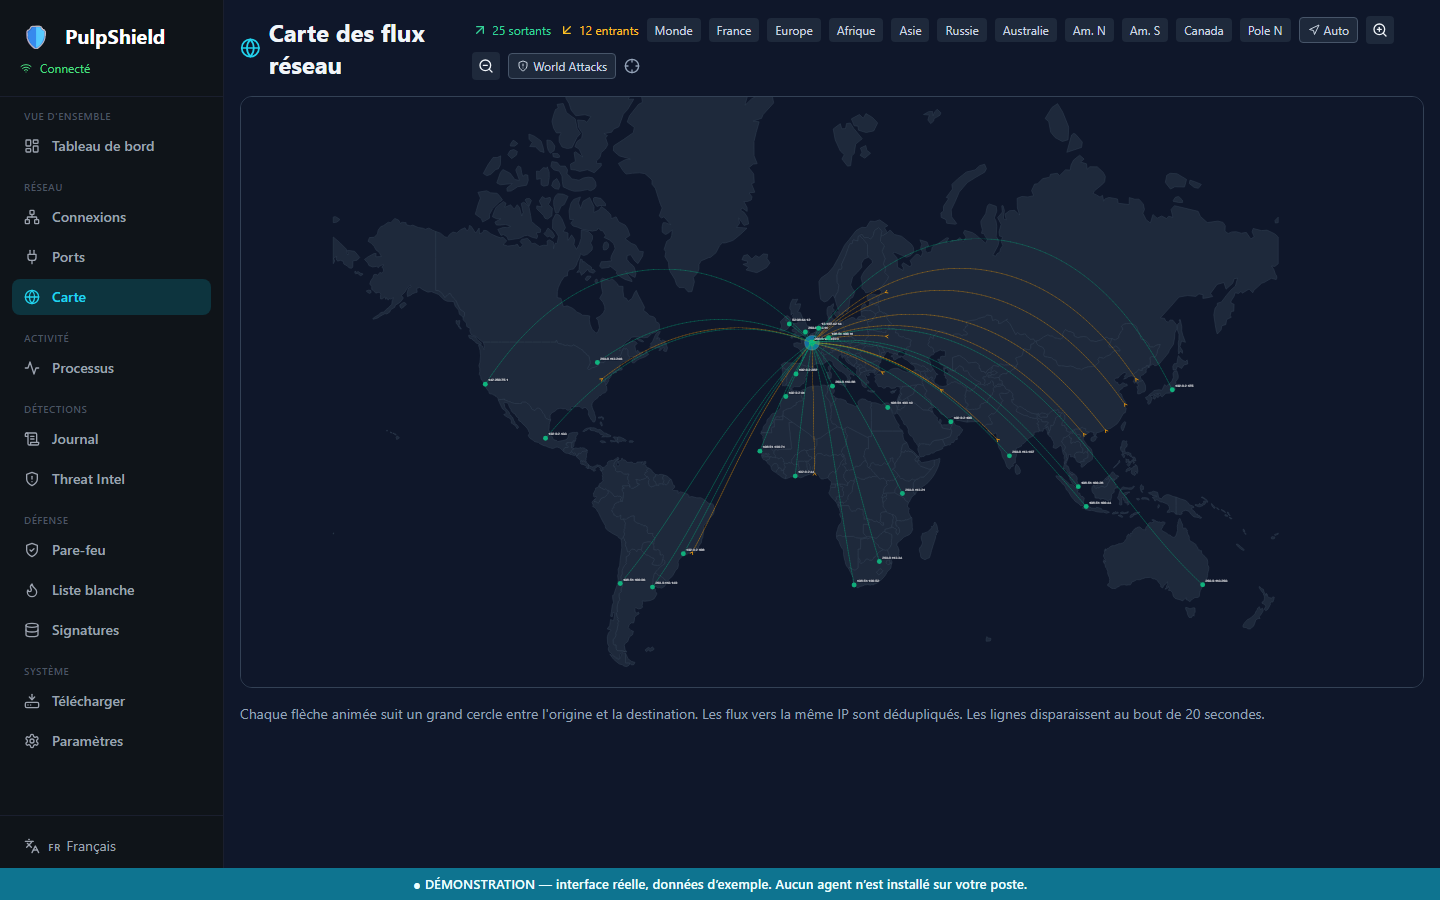
PulpShield dashboard: posture score, agent footprint and attacks detected over 24 hours World map of network flows: 25 outbound flows to Africa, Asia and South America, 12 hostile inbound flows

Where your traffic actually goes. Every outbound flow is drawn in green, every inbound one in amber. A connection to a country you do no business with stands out immediately.

Try the live interface See the interface Sample data — no agent is installed on your machine.
Free trial

Download it, try it for three months, then subscribe

  1. 1
    Download the agent for your operating system and install it on the machines you want to protect.
  2. 2
    Get a 3-month trial key — every feature, no credit card.
  3. 3
    Convinced? Subscribe per endpoint; your data stays hosted in France 🇫🇷.
🪟

Windows 10/11 — x64

Guided installer · runs as a service

PulpShield-Setup.exe

Download
🐧

Linux — x64

Debian, Ubuntu, VPS

pulpshield-agent-linux-x64.tar.gz

Download
🍎

macOS — Universal

Apple Silicon / Intel

pulpshield-agent-macos-universal.tar.gz

Download
Publisher note: upload the signed binaries (Windows code-signing certificate / Apple notarization) to these /downloads/… paths before going public — otherwise SmartScreen and antivirus will block them.
About

French cybersecurity, built in France

PulpShield is published by SAS Digitigrade Studio, a French company based in Montélier, Drôme. Our conviction: smaller businesses deserve professional-grade protection that is sovereign and affordable — without depending on foreign vendors.

The project is led by Nicolas Hesse, founder, in the Drôme region of France, who designed PulpShield as the sovereign answer to the security needs of small businesses.

👤

Nicolas Hesse

Founder — Drôme, France 🇫🇷

SAS Digitigrade Studio · 26120 Montélier

FAQ

Frequently asked questions

Is PulpShield a French solution, hosted in France?

Yes. PulpShield is published by a French company and deploys on-premise: your data stays in France, with no mandatory foreign cloud.

Is it complicated to install?

No. One lightweight agent per machine (Windows, Linux, macOS), then you open the interface locally. No advanced skills needed.

Does PulpShield help with NIS2 and CRA compliance?

Yes: incident detection, traceability and reporting address NIS2 and Cyber Resilience Act requirements. PulpShield is itself built secure by design.

How is this different from an antivirus?

Antivirus blocks known files. PulpShield detects attack behaviour — command-and-control traffic, exfiltration, lateral movement — that antivirus never sees.

What does it cost? Is there a trial?

A free 3-month trial, then a per-endpoint subscription from €5 per endpoint per month. Volume discounts and a partner programme for MSPs.

Does my data go to a foreign cloud?

No. Deployed on-premise, your data never leaves your organisation — including when you enable the optional AI analysis, since the Mistral models run on your own servers.

Protect your business, on your own terms.

Ask for a demo or a quote sized to your estate.

contact@pulpshield.com